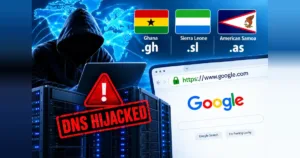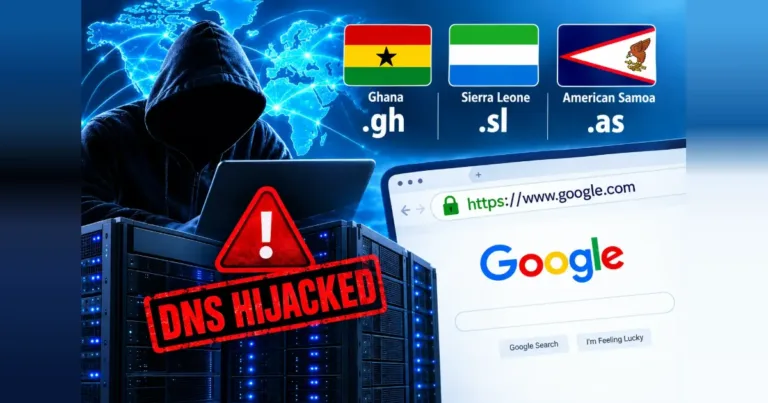
Attackers have compromised the country-code domain registries for Ghana, Sierra Leone and American Samoa, allowing them to alter domain name system (DNS) records and obtain unauthorised https certificates for several Google domains, global brands and widely used online services.
In a statement on Tuesday, Google said the third-party infrastructure responsible for the three country-code top-level domains (ccTLDs) were compromised but its systems were intact.
“These incidents did not involve a compromise of Google’s systems; rather, attackers compromised the third-party ccTLDs, putting any domain ending in .gh, .sl, or .as at risk,”said Google.
DNS acts much like the internet’s address book. It tells a computer where to find a particular website when a user enters a domain name.
According to Google, the attackers modified authoritative DNS records for selected domains within the affected namespaces. This gave the attackers enough control to pass automated checks used by certificate authorities (CAs) when issuing https certificates, which allow browsers to establish encrypted connections with websites and display the familiar padlock symbol.
Under normal circumstances, a certificate authority verifies that an organisation controls a domain before issuing a certificate. In this case, however, the attackers had compromised the DNS infrastructure used to demonstrate that control. As a result, legitimate certificate authorities issued certificates that the attackers were not authorised to possess.
Google described these as unauthorised https certificates covering several of its domains, as well as domains belonging to other organisations. It said there was no indication that the CAs did anything wrong, as they were just following their normal procedures.
“During these hijacks, attackers modified authoritative DNS records and obtained unauthorized https certificates covering several Google domains, as well as domains belonging to other organizations. Due to the nature of the attacks, we have no reason to believe the Certification Authorities (CAs) that issued the impacted certificates did anything wrong,” the company said.
A valid https certificate can make an attacker-controlled website appear much more convincing. If an attacker controls DNS for a domain and also obtains a certificate for that domain, there is a potential pathway for the attacker to redirect users toward infrastructure under their control while maintaining an apparently valid https connection. That could potentially be used in sophisticated phishing, traffic interception or impersonation attacks.
Ars Technica reported that the number of affected organisations and the full scope of the incident were not immediately clear.
Google said Chrome immediately moved to block the unauthorised certificates associated with its own properties through a mechanism known as CRLSets.
The company also worked with the certificate authorities involved to have the certificates revoked, providing protection for users of browsers and other clients that rely on those revocations.
“As part of our usual incident response process, we immediately acted to protect users by blocking the use of unauthorized certificates for Google properties in Chrome via CRLSets. We also worked with the issuing CAs to ensure the certificates were revoked to protect users in clients other than Chrome,” it said.
Google then examined certificate transparency (CT) logs, which publicly record certificates issued by trusted certificate authorities, uncovering additional organisations believed to have been affected, including major global brands and widely used online services. Chrome subsequently blocked those certificates as well.
Google has cautioned organisations not to depend entirely on browser companies to identify and block malicious certificates. The complexity of DNS hijacking means it cannot guarantee that every affected domain has been identified and Chrome’s intervention does not automatically provide the same protection to users of non-Chrome browsers and other software.
Google is therefore encouraging organisations to continuously monitor certificate transparency logs for their domains.
It is also recommending that domain owners publish restrictive certificate authority authorization (CAA) records, allowing domain owners to specify which certificate authorities are permitted to issue certificates for their domains.
Google cautions that CAA cannot completely prevent certificate issuance while an attacker has active control of DNS, but restrictive CAA policies can provide an additional layer of protection once DNS control has been restored.
For businesses, banks, telecommunications companies, government agencies and other organisations whose operations depend heavily on online services, the incident highlights the importance of monitoring certificates rather than simply assuming that https means everything is secure.
The full details of the compromise, including the identities of the attackers, the exact number of affected domains and whether all unauthorised certificates have been identified, remain unclear but Google says it will continue working with the wider internet-security community to strengthen the https ecosystem and reduce the risks created by temporary DNS and routing compromises.